Why AI Model Lifecycles Are Becoming a Platform Risk
GitHub’s October 19 Copilot retirements and policy API show why AI model versions need ownership, evaluation gates and controlled migration.
GitHub’s October 19 Copilot retirements and policy API show why AI model versions need ownership, evaluation gates and controlled migration.
On 19 October 2026, GitHub retired six models across most Copilot experiences and pointed users toward newer alternatives. On the same day, it made REST endpoints for model policies generally available at enterprise, team, app and organization levels. The combination is more important than either update alone: enterprise AI models are no longer static product choices. They are versioned dependencies that can disappear, change behavior and require coordinated migration.
For platform leaders, the practical question is no longer simply which model performs best. It is whether the organization can identify where a model is used, test a replacement, change policy, observe the rollout and reverse course without interrupting critical work.
GitHub’s October 19 retirement notice covered Gemini, OpenAI and xAI models used across chat, inline edits, agent modes and code completion. GitHub provided suggested alternatives, but it also warned that enterprise administrators might need to enable those replacements through model policies. A technically available successor can still be operationally unavailable if policy and deployment controls are not aligned.
Provider schedules also differ. OpenAI’s current deprecations page says several GPT-4 series snapshots, including fine-tuned versions built on them, are scheduled for removal on 14 January 2027. Anthropic’s model lifecycle documentation lists Claude Sonnet 4.5 as deprecated on 30 September 2026 with retirement scheduled for 30 November. Amazon Bedrock’s legacy-model policy adds another layer: lifecycle status can vary by region, migration is not automatic, new provisioned throughput is unavailable for legacy models, and extended access may carry higher pricing.
The implication is that a model identifier is part of an application’s operating contract. Replacing it can alter output structure, tool behavior, latency, token usage, safety characteristics and cost even when the business workflow appears unchanged.
Every production use should record the exact model or alias, provider, access path, region, application owner, business purpose, data constraints and retirement date. It should also link to the prompt or agent configuration, evaluation suite, incident history and approved fallback. That turns scattered vendor notices into an actionable dependency map.
This complements the broader enterprise AI control plane. Identity and permissions determine what an AI system may do; lifecycle records determine whether the component doing that work is still supported and behaving as approved.
A vendor-recommended replacement is a starting point, not acceptance evidence. Teams should run representative tasks against the candidate model and compare the measures that matter for the workflow: task success, structured-output validity, tool-call accuracy, refusal behavior, latency and total cost. Security-sensitive applications also need adversarial cases and confirmation that logging, data handling and regional controls remain intact.
The safest sequence is staged. First, reproduce the current workload with pinned prompts, tools and schemas. Next, shadow a portion of traffic or replay a controlled test set against the replacement. Then route a limited production cohort through the new model while monitoring exceptions and human corrections. Only after acceptance should the organization change the default and retire the old route.
This testing layer is especially important for agents. As WiredBusiness has examined in its coverage of AI agent governance beyond the model, tool execution, identity and independent monitoring must remain enforceable even when the reasoning model changes.
GitHub’s new Copilot model policy API illustrates why lifecycle work belongs in platform engineering. Central teams can define supported defaults, while organizations or application teams retain bounded control where delegation is appropriate. The key is to separate “the vendor offers this model” from “this enterprise has approved it for this workload.”
An internal allowlist should therefore carry an owner, scope, approval evidence and expiry or review date. A lifecycle event should automatically create work for the responsible team, show the affected applications and set a deadline with enough time for testing. Where providers expose lifecycle data programmatically, such as Bedrock’s model lifecycle fields, platform tooling can monitor status rather than depend entirely on inbox notices.
Fast model turnover is likely to remain a feature of the market. Organizations that treat every retirement as an emergency will accumulate brittle integrations, inconsistent policy and rushed testing. Those that make model migration a normal platform capability can adopt improvements without surrendering operational control.
The durable advantage will not come from offering employees the longest model menu. It will come from knowing which models matter, proving that replacements work and changing them on a schedule the business can govern.
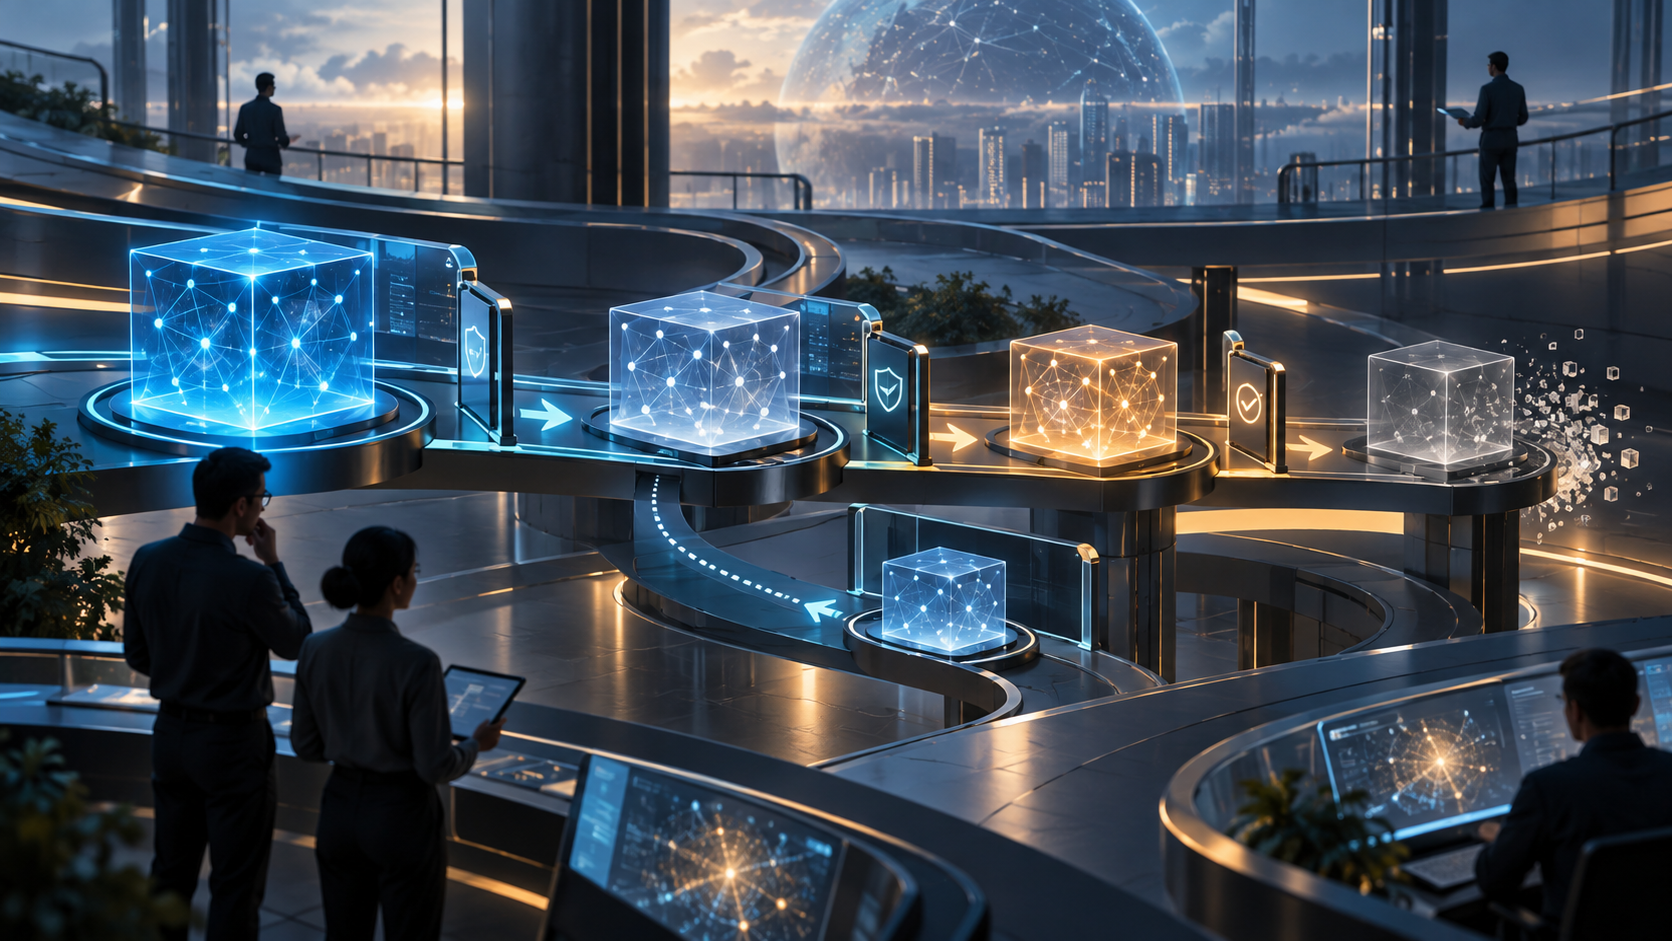
Header image: Original AI-generated editorial illustration created for WiredBusiness. It represents model evaluation, migration and retirement controls and does not depict a specific vendor product or production environment.
Join industry leaders and innovators who rely on us for exclusive insights, interviews, and trends shaping the future of business and tech — straight to your inbox.