Why AI Agents Need Their Own Security Identity
Microsoft and Palo Alto Networks guidance shows why enterprises should treat every AI agent as a first-class security principal with limited, revocable authority.
Microsoft and Palo Alto Networks guidance shows why enterprises should treat every AI agent as a first-class security principal with limited, revocable authority.
Enterprises are beginning to treat AI agents as more than software features. An agent can read documents, call APIs, execute code, update records and pass work to another agent. That makes it operationally useful, but it also means the familiar model of securing only the human user and the application is no longer enough. An agent that can act needs an identity that can be authenticated, restricted, monitored and revoked.
The shift is visible across recent security guidance. Microsoft’s October 1 2026 Digital Defense Report overview describes agents as connected components that interact with enterprise data, applications, APIs and tools. Microsoft highlights agent identity, appropriate access, authentication between agents, attribution and revocation as core security concerns. The business implication is clear: deploying agents without an identity architecture creates a new class of unowned access.
A common shortcut is to let an agent operate with the credentials or broad permissions of the employee who launched it. That is convenient, but it obscures who—or what—performed an action. It also exposes every resource available to the user even when the agent needs only a small subset.
Microsoft’s July 16 least-privilege guidance for AI agents recommends treating every agent as a first-class principal: assign a lifecycle-managed identity, explicit roles, tightly scoped permissions and a defined tool manifest. This gives security teams a practical control point. If an agent changes function, ownership or risk level, its access can change without disabling the human employee or disrupting unrelated systems.
Separate identity also improves accountability. Logs should distinguish whether a person acted directly, an agent acted on its own authority, or an agent acted on behalf of a person. Without that distinction, incident responders may see a valid credential and miss the automated decision chain behind it.
Prompt injection and unreliable outputs matter, but their business impact depends heavily on what an agent can reach. A manipulated agent that can only draft a response creates a different exposure from one that can run terminal commands, retrieve secrets, modify production code or approve a financial workflow.
Palo Alto Networks’ September 25 announcement about securing AI coding agents focuses on that execution boundary. The company says coding agents can access developer terminals, source repositories, APIs and Model Context Protocol tools, creating endpoint activity that conventional controls may not interpret in context. Its proposed controls inspect prompts, tool calls and network interactions, then apply policy before an action executes. These are vendor claims about Palo Alto Networks products, but the architectural lesson is broader: tool invocation needs its own enforcement layer.
An identity record alone does not make an agent safe. Organizations also need boundaries around data, tools, destinations and the duration of access. Microsoft’s May 14 defense-in-depth guidance argues that separate agent identity enables least privilege, lifecycle governance and meaningful observability. It also frames agent security as a layered problem involving permissions, escalation, logging and isolation.
For business leaders, this suggests a minimum operating model. Maintain an inventory of deployed agents and owners. Issue non-shared identities. Grant only the permissions required for a defined task. Restrict which tools each agent can call and where data can travel. Use short-lived credentials where practical. Log the agent, initiating user, requested action, tool and outcome. Finally, test whether access can be revoked quickly without breaking an entire workflow.
The biggest risk may be agent sprawl rather than one dramatic exploit. Teams will create specialized agents for coding, sales, finance, support and operations. Some will be experimental; others will quietly become critical infrastructure. If ownership, permissions and retirement are not managed from the start, dormant agents and stale integrations will accumulate like service-account debt.
A useful approval process should therefore ask four questions before deployment: Who owns the agent? What exact resources and tools can it use? Which actions require human confirmation? What evidence will show whether it behaved as intended? Those questions connect cybersecurity to operating accountability rather than reducing it to a product configuration.
AI agents are becoming participants in enterprise workflows. The security model must recognize them accordingly. The organizations that assign agents distinct identities, bounded authority and auditable actions will be better positioned to scale automation without losing control over who can do what.
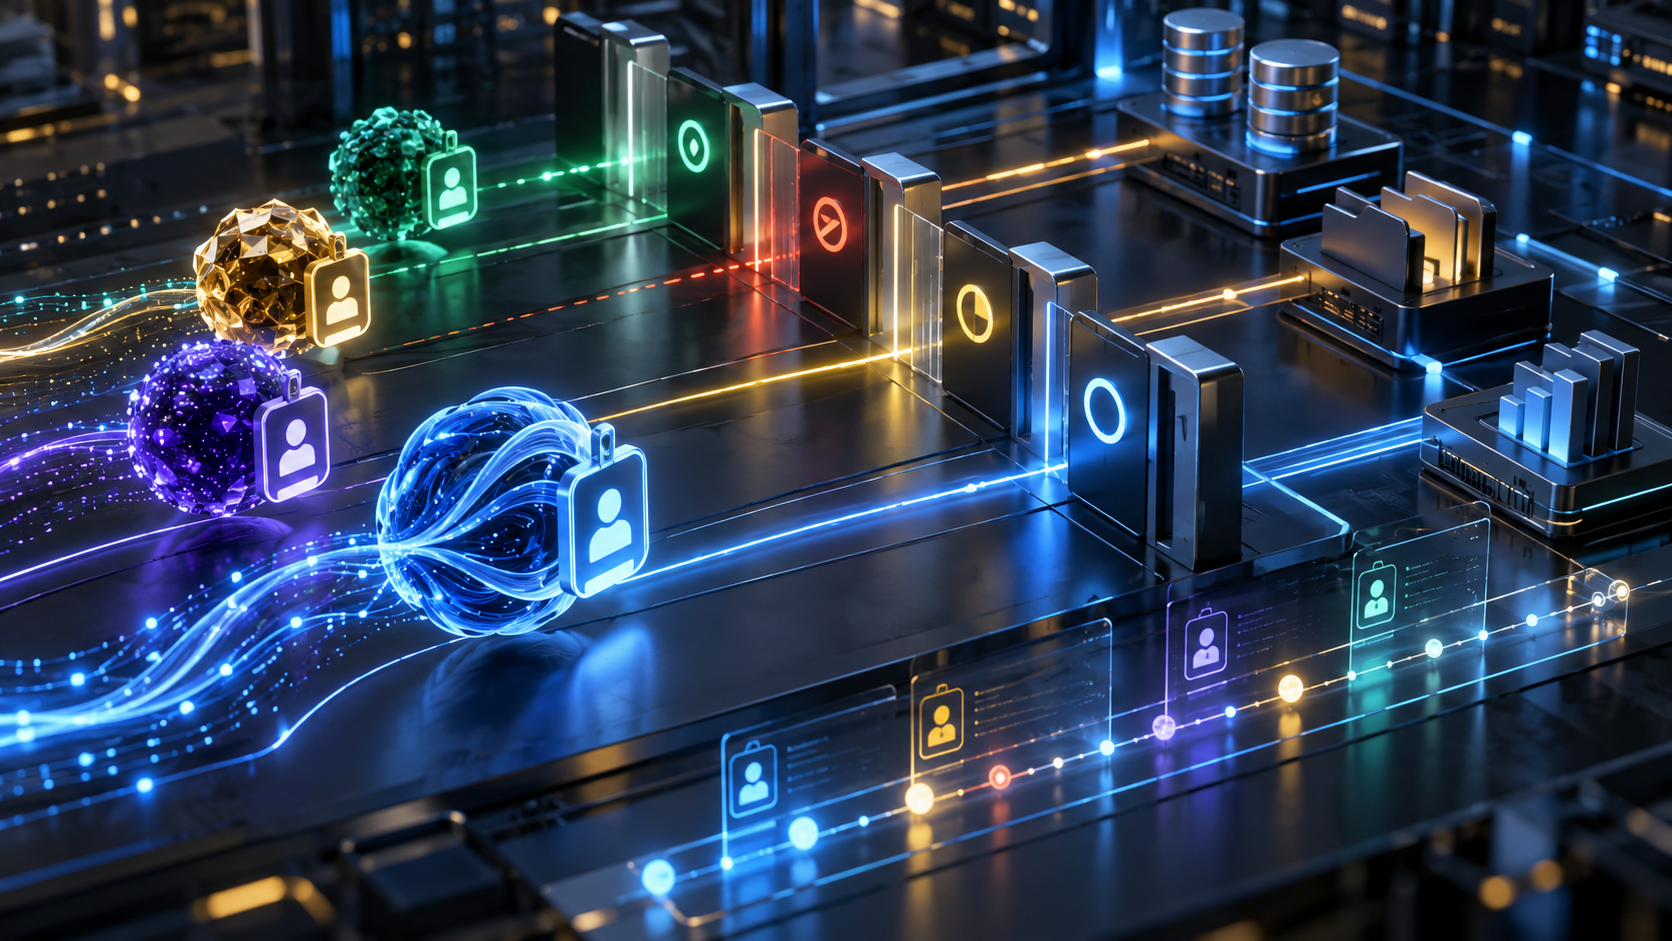
Header image: Original AI-generated editorial illustration created for WiredBusiness. It represents agent identity and least-privilege access controls and does not depict a specific product or deployment.
Join industry leaders and innovators who rely on us for exclusive insights, interviews, and trends shaping the future of business and tech — straight to your inbox.