Why SBOMs Are Becoming Operational Software Systems
NIST guidance, GitHub attestations and OpenSSF tooling show why enterprises need SBOMs to function as live, verifiable systems of record—not release-time paperwork.
NIST guidance, GitHub attestations and OpenSSF tooling show why enterprises need SBOMs to function as live, verifiable systems of record—not release-time paperwork.
A software bill of materials was once treated like a packing list: generate it at release time, store it for an audit and retrieve it when a customer asks. That model is becoming inadequate. Modern applications are assembled continuously from open-source packages, containers, build actions and internal services. The useful question is no longer whether an SBOM exists. It is whether an organization can connect the right component record to the exact artifact running in production and act when the risk around that component changes.
Across 2026 guidance and tooling, SBOMs are moving from static compliance documents toward operational data systems. That shift has implications for software platforms, procurement and executive risk management: producing a file is the beginning of the control, not the end.
The National Institute of Standards and Technology's December 17, 2025 draft update to the Secure Software Development Framework describes a common set of practices that organizations can integrate into their software-development lifecycles. NIST presents the framework as a way for producers to reduce vulnerabilities and for acquirers to communicate with suppliers using shared terminology.
That lifecycle perspective matters. A component list detached from the build that produced it can become stale as soon as a package is upgraded or a container is rebuilt. An operational system therefore needs stable identifiers for artifacts, automated generation in the build pipeline and retention rules that let teams recover the record associated with a particular release. The governance object is not simply “the application”; it is the application version, its build and the components actually shipped together.
GitHub's current artifact-attestation documentation shows how the data can be bound more closely to software delivery. GitHub says an attestation creates a cryptographically signed claim about where and how an artifact was built, including its workflow, repository, commit and triggering event. An associated SBOM can be included with that evidence.
The distinction is important. An SBOM says what a build contains; provenance links the output to the process that produced it. Neither proves that software is safe. GitHub explicitly warns that attestations must be verified and evaluated against an organization's own policy. Together, however, the two records give security and procurement teams a stronger basis for deciding whether an artifact came from an approved pipeline and whether its dependencies meet policy.
Generating documents is easier than operating them at enterprise scale. A large organization may receive SPDX and CycloneDX records from hundreds of internal teams and suppliers. Those records need to be ingested, normalized and matched to deployed assets. New vulnerability information then has to be mapped back to affected products without rescanning every release from scratch.
The Open Source Security Foundation's August 28 announcement that BOMHort joined its sandbox illustrates the direction of travel. OpenSSF describes the project as a Kubernetes-native platform that ingests, normalizes and visualizes SBOMs, supports common formats and connects component data with vulnerability and license analysis. Those are project claims rather than independent performance findings, but the architecture reflects the operational challenge: the enterprise needs a queryable system of record, not a folder full of JSON files.
An operational SBOM system earns its keep when conditions change. A newly disclosed vulnerability should trigger a reliable answer about which released products contain the affected version, where those products are deployed and who owns remediation. A supplier change should be traceable across builds. A procurement review should distinguish vendors that merely deliver an inventory from those that bind evidence to releases and keep it current.
This makes SBOM data a shared business asset. Engineering creates much of it; security evaluates it; legal and compliance teams use license and regulatory evidence; procurement asks suppliers for it; operations connects it to running systems. If each function keeps a separate copy, inconsistencies grow. A common platform can preserve the underlying evidence while exposing different workflows to each team.
Technology leaders can start with five decisions. Define the authoritative identifier for every releasable artifact. Generate the SBOM inside the controlled build process. Bind it to provenance and verify the attestation before deployment. Ingest the record into a searchable inventory linked to product owners and environments. Finally, measure the time from new risk information to an accurate impact decision and verified remediation.
Those steps turn SBOM adoption from a document project into an operating model. The goal is not to accumulate more component data. It is to create a dependable loop from build evidence to deployed inventory, risk decision and corrective action. Organizations that make that loop routine will be better prepared for both supplier questions and the next urgent software incident.
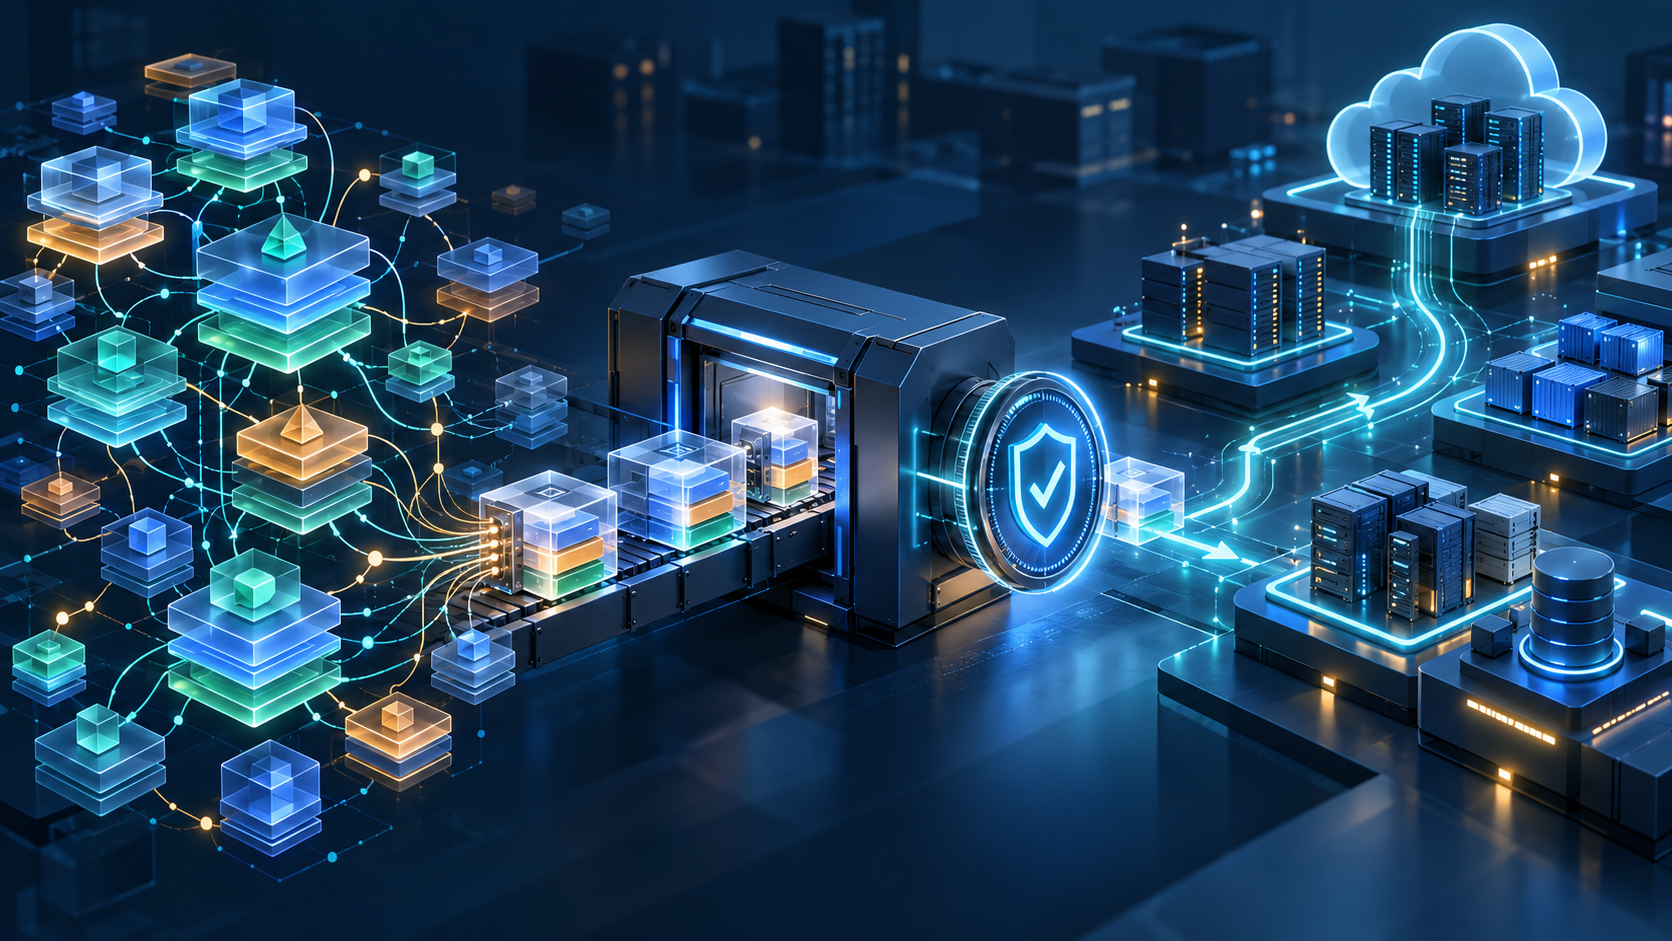
Header image: Original AI-generated editorial illustration created for WiredBusiness. It is illustrative and does not depict a specific product or deployment.
Join industry leaders and innovators who rely on us for exclusive insights, interviews, and trends shaping the future of business and tech — straight to your inbox.